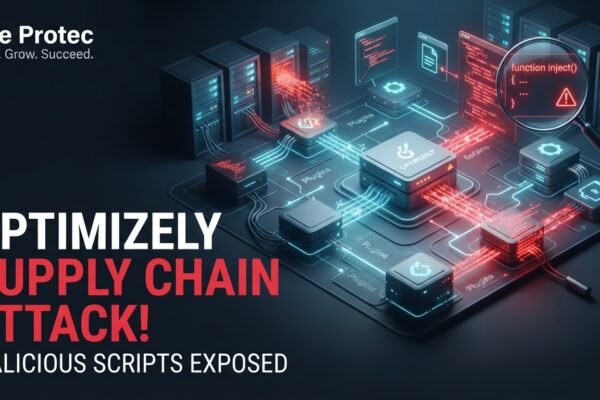
Inside the Optimizely supply chain attack and its malicious scripts
See how the Optimizely supply chain attack put 178 organizations’ trusted scripts at risk, what payloads did, and how defenders should respond with confidence.
See how the Optimizely supply chain attack put 178 organizations’ trusted scripts at risk, what payloads did, and how defenders should respond with confidence.
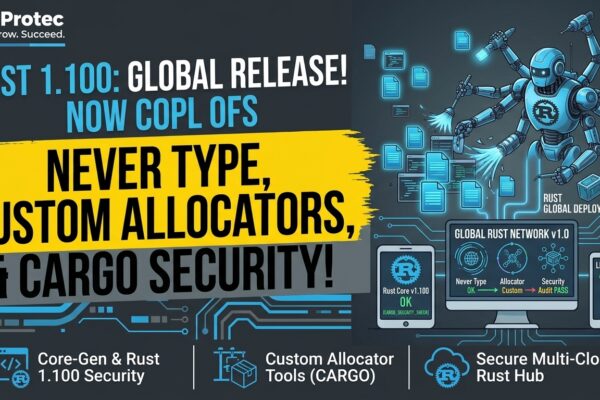
Rust 1.100 stabilizes the never type, unlocks custom allocators, adds DropGuard, and gives Cargo a practical dependency cooldown for safer production builds.
Learn seven practical GitHub Actions security controls to limit tokens, pin dependencies, isolate pull requests, protect secrets, and harden deployments.
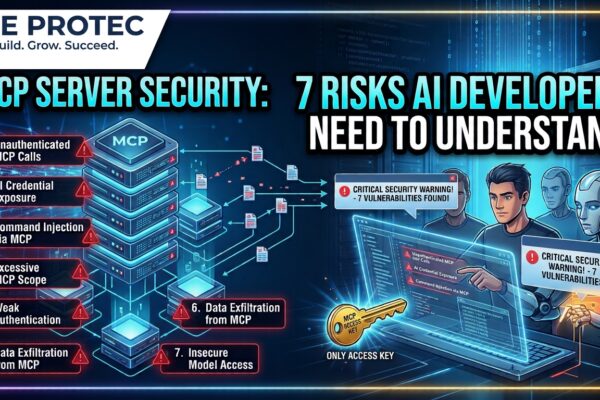
Learn why MCP server security matters as AI agents reach sensitive tools, and how developers can reduce authentication, permission, and supply-chain risks.
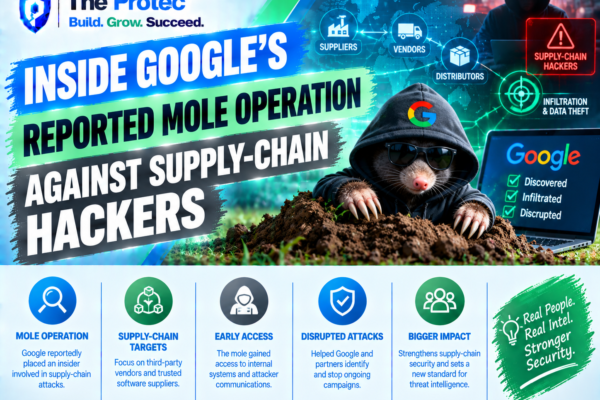
Google reportedly gained inside visibility into the hackers behind a major software supply-chain attack. Here’s what the Google Mole Operation could reveal about the hackers and why it matters.
n 2026, supply chain attacks have become one of the most dangerous and fastest-growing cybersecurity threats. Businesses are no longer just defending their own systems—they must now protect an entire ecosystem of vendors, partners, and third-party services.