C is usually associated with operating systems, embedded devices, databases, and performance-critical infrastructure—not login forms, dashboards, or database-backed websites. Yet the Modern Web App in C concept challenges that assumption, showing how the same language that powers large parts of the internet’s foundation can also power an application at the HTTP layer.
A developer willing to work closer to the machine can accept network connections, parse requests, dispatch routes, query SQLite, and generate HTML without PHP, Node.js, or Python. Projects such as Joris Vink’s Kore web framework show that C web development can extend well beyond a toy socket server. Kore provides a practical case study because it combines native C handlers with web-oriented infrastructure, while leaving application logic under the developer’s control.
That does not mean C is automatically the fastest or best choice. The more useful question is how far developers can take a modern web app in C, what the architecture looks like, and whether the control gained is worth the engineering cost.
What the Original C Web Project Actually Demonstrates
Kore is a C programming web framework and server created for building web applications in C. Its repository demonstrates native request handlers, routing, configuration, HTTP serving, WebSockets, background tasks, and integrations intended to avoid rebuilding every protocol detail from scratch. It is better understood as infrastructure for C language backend development than as evidence that every application should abandon established frameworks.
The project proves that a functional web application does not require an interpreted runtime. A compiled binary can receive requests and return dynamic responses. It does not, by itself, establish that C will outperform every Laravel, Node.js, or Python application under realistic workloads. Database latency, caching, application design, network behavior, and deployment configuration often matter more than language-level speed.
C Web Application Architecture, Step by Step
1. Accepting HTTP Connections
At the lowest level, a web server in C creates a socket, binds it to an address and port, listens for traffic, and accepts client connections. A C socket programming tutorial might implement this directly with operating-system APIs. A serious application is usually better served by an established library or C programming web framework that already handles event loops, connection lifecycles, timeouts, and partial reads.
Modern deployments also tend to place the application behind a reverse proxy. The proxy can terminate TLS, negotiate HTTP/2 or HTTP/3, enforce request-size limits, and pass conventional HTTP/1.1 traffic to the C process. This keeps complex internet-facing protocol work out of application code.
2. Parsing Requests Safely
An HTTP server in C must interpret the method, path, headers, query string, cookies, and optional request body. Parsing is one of the most dangerous parts of low-level web programming. Requests can arrive in fragments, contain conflicting length headers, use unusual encodings, or deliberately target parser inconsistencies.
Writing a small parser is educational, but production-facing software should use a maintained parser with clearly defined size limits. Every length must be checked before copying data, and malformed requests must fail closed rather than being partially accepted.
3. Dispatching Routes and Middleware
C routing and middleware follow the same conceptual model used by higher-level frameworks. A routing table maps combinations such as GET /articles or POST /login to handler functions. Middleware can run before or after those handlers to perform authentication, logging, rate limiting, security-header generation, or request tracing.
Unlike Laravel or Express, plain C supplies no standard routing convention. Developers must choose a framework, implement a dispatcher, or use generated lookup tables. Explicit function calls are predictable, but the project needs consistent conventions before it grows.
4. Validating Application Input
Request parsing only establishes structure. Application validation determines whether an email address, identifier, page number, or uploaded file is acceptable. Values should be validated against allowlists and strict ranges before business logic uses them. Numeric conversions need overflow checks, strings need explicit maximum lengths, and uploaded content needs both size and type controls.
This boundary is especially important in C because an unchecked length is not merely a bad user experience—it can become memory corruption.
5. Adding SQLite Database Integration in C
A compact C programming project can use SQLite without running a separate database service. The application opens a database connection, prepares statements, binds validated parameters, steps through results, and finalizes statements. The official SQLite C interface documentation describes this native API.
A SQLite web application is well suited to local tools, embedded products, prototypes, and read-heavy services with controlled write concurrency. Prepared statements are essential: SQL commands should never be assembled by concatenating raw request data. Larger deployments may require a client-server database, connection management, migrations, backups, and replication.
6. Generating HTML and Errors
HTML generation in C can be as simple as writing static fragments into a bounded response buffer. A more maintainable design separates templates from handlers and escapes all untrusted values according to their output context. HTML text, attributes, URLs, JavaScript, and JSON require different escaping rules.
Handlers should return structured status values so one error layer can produce consistent responses. Clients should receive an appropriate status code and a generic message, while detailed diagnostics go to protected logs. Allocation failures, missing records, database locks, invalid methods, and oversized requests all need deliberate paths.
What Should Be Written Directly in C?
Developers can implement sockets, an event loop, HTTP parsing, routing, sessions, database access, templates, and static-file delivery directly in C. That is valuable for learning systems programming for the web, but it creates a large security and maintenance obligation.
A practical build should reuse mature components for HTTP parsing, cryptography, TLS, compression, and database access. CGI programming in C remains possible, but launching or coordinating processes per request is rarely the best foundation for a responsive modern service. An embedded or event-driven lightweight web server is generally more suitable.
As of October 2026, modern web development tools around C include mature Clang and GCC diagnostics, sanitizers, profile-guided optimization, fuzzing engines, static analyzers, containers, and hardened reverse proxies. C23 language adoption is advancing, but toolchain compatibility still needs to be checked across deployment targets.
Why Developers Consider a Modern Web App in C
C offers fine-grained control over allocation, data layout, system calls, concurrency, and dependencies. A compiled service can have a small deployment footprint, predictable startup behavior, and modest baseline resource use. Portability also makes C attractive when a backend must run on an appliance, constrained gateway, industrial controller, or unusual operating system.
That control creates opportunities for backend performance optimization. Developers can avoid unnecessary copies, pool allocations, stream large responses, and tune data structures around a known workload. However, manually managing memory does not guarantee speed. A blocking database query or inefficient algorithm remains slow regardless of how quickly the surrounding C code executes.
C vs PHP, Node.js, and Python for Web Development
C vs PHP and Laravel
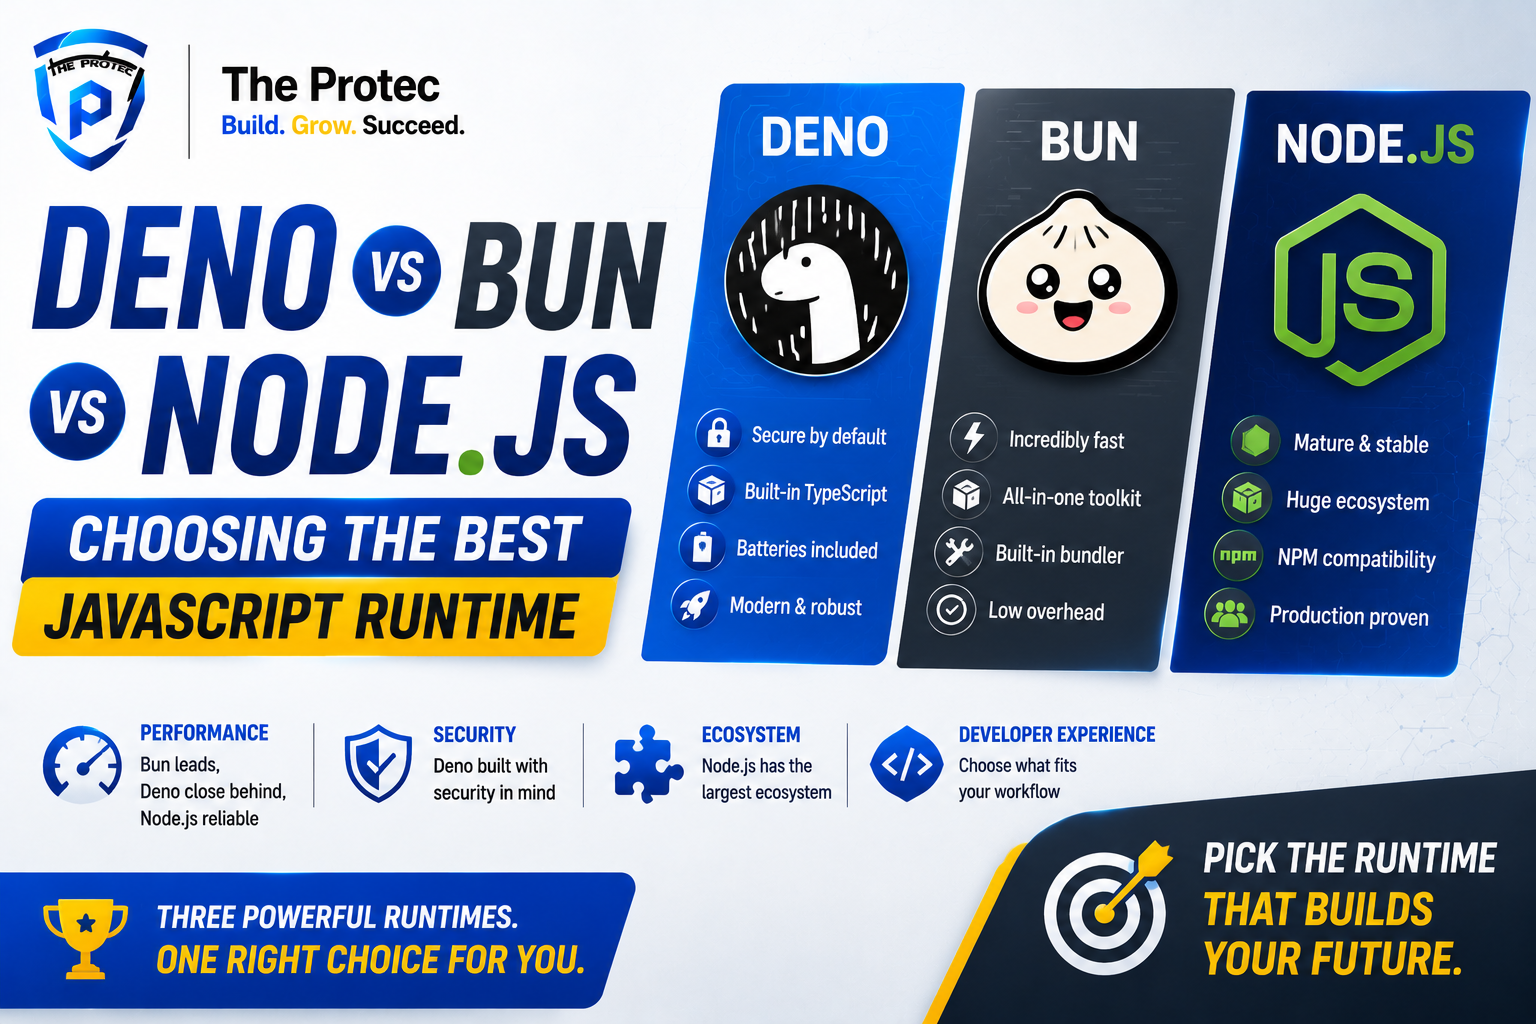
In C vs Laravel, Laravel wins decisively on development speed for conventional business applications. It includes routing, validation, authentication patterns, templating, database migrations, queues, testing utilities, and a large package ecosystem. PHP also isolates many memory-management concerns from application developers.
C can produce a smaller, tightly controlled service, but teams must build or integrate features Laravel provides by default. Maintenance becomes harder when only a few engineers understand the custom runtime and ownership rules.
C vs Node.js
C vs Node.js is less straightforward than raw execution speed suggests. Node.js has an effective asynchronous I/O model, extensive web libraries, and excellent support for JSON-centric APIs and real-time services. C provides deeper control and can reduce runtime overhead, but asynchronous state management, cancellation, backpressure, and resource cleanup require careful design.
C vs Python for Web Development
Python frameworks make prototypes and data-driven services faster to develop. Their ecosystems cover authentication, administration, testing, machine learning, and observability. A C service may use fewer resources for a specialized task, but Python usually offers better productivity for changing product requirements.
Scalability depends on architecture in every language. Multiple processes, caching, queues, indexes, load balancing, and database design commonly outweigh runtime differences. High-performance web applications emerge from measurement and sound design, not language choice alone.
Memory-Safe Web Development Is the Central Challenge
C is not memory-safe by default. A C web server security review must account for buffer overflows, out-of-bounds reads, use-after-free defects, integer overflow, double frees, format-string vulnerabilities, and uninitialized memory. Unsafe string functions and ambiguous ownership rules sharply increase risk.
Web-specific threats add another layer: SQL injection, cross-site scripting, path traversal, request smuggling, resource exhaustion, weak password storage, insecure cookies, broken authorization, and session fixation. Authentication code is particularly unsuitable for casual reinvention.
Risk can be reduced through disciplined engineering:
- Use established HTTP, TLS, and cryptographic libraries rather than custom implementations.
- Compile with aggressive warnings and treat important warnings as errors.
- Run AddressSanitizer, UndefinedBehaviorSanitizer, and leak detection during testing.
- Fuzz request parsers, decoders, routing logic, and file-handling boundaries.
- Use prepared SQL statements and context-aware output escaping.
- Apply explicit limits to headers, bodies, uploads, connections, and processing time.
- Centralize allocation ownership and cleanup conventions.
- Run as an unprivileged account with minimal filesystem and network access.
- Patch dependencies and test malformed input continuously.
These practices improve safety, but they do not transform C into a memory-safe language. For internet-facing applications, that residual risk must be part of the technology decision.
Deployment and Performance Without Unsupported Claims
A sensible production-shaped deployment places the C service behind a maintained reverse proxy, runs it with least privilege, and exposes only the required local port or Unix socket. The environment should include structured logs, health checks, metrics, crash reporting, request deadlines, graceful shutdown, and restart supervision.
Benchmarking should model real work: TLS, representative payloads, database queries, concurrent clients, error responses, and memory pressure. Requests per second from a minimal plaintext handler do not predict application performance. Profile first, optimize measured bottlenecks, and compare complete systems rather than language loops.
When Building a Website Using C Makes Sense
Building a website using C is reasonable for education, embedded administration panels, network appliances, specialized infrastructure, existing C products, and services with measured resource constraints. It can also be an excellent way to understand HTTP, sockets, parsers, databases, and operating-system behavior.
For a typical commerce site, content platform, internal dashboard, or fast-changing SaaS product, a mature PHP, Node.js, Python, Java, Go, or other established web stack is usually the better engineering choice. Use C when its control and portability solve a concrete problem—not simply because the premise makes compelling technology news.
Frequently Asked Questions
Can you build a complete web application in C?
Yes. C can implement an HTTP server, routing, middleware, authentication, database access, HTML responses, APIs, and static-file delivery. Frameworks and libraries make this far more practical than implementing every component manually.
Is a C web application faster than Node.js or PHP?
Not automatically. C offers optimization opportunities and low runtime overhead, but application performance depends on algorithms, database access, caching, I/O, concurrency, and deployment. Only representative benchmarks can establish an advantage.
Is C suitable for an internet-facing web server?
It can be, but the security burden is substantial. Maintained libraries, strict limits, fuzz testing, sanitizers, prepared statements, reverse-proxy protection, and least-privilege deployment are baseline requirements.
Is SQLite appropriate for a C web application?
SQLite is effective for embedded applications, local services, prototypes, and workloads with moderate write concurrency. Applications with heavy concurrent writes or distributed requirements may need a client-server database.
Should beginners try web development without frameworks?
Implementing a small HTTP server in C is an excellent learning exercise. Beginners should avoid exposing it directly to untrusted internet traffic and should use a maintained framework or server for applications that store sensitive data.